Microsoft Uncovers USDT-Funded Phishing Network Targeting 75,000 Organizations
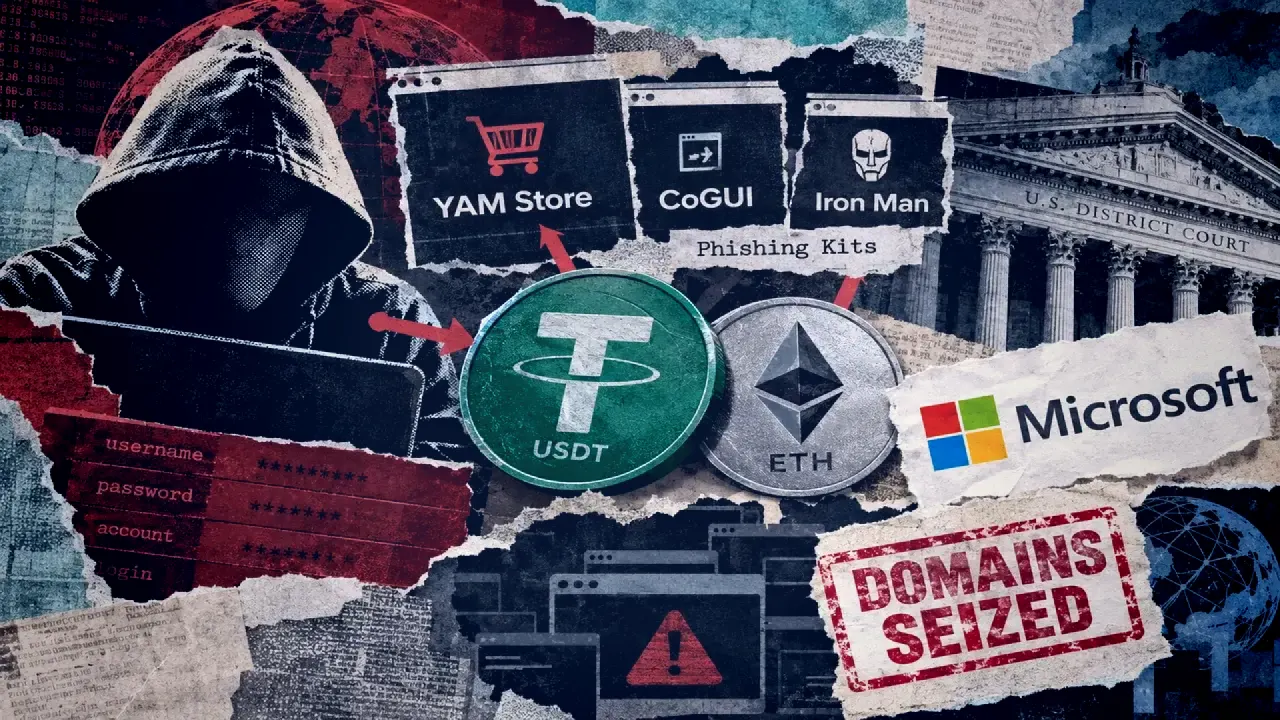
Microsoft has exposed a significant phishing network that utilized Tether (USDT) as funding, impacting around 75,000 organizations. The operation has resulted in various domain seizures and the shutdown of phishing-kit services, although the extent of asset freezes remains unclear.
Details of the Operation
The phishing network's operations have raised alarms within the cybersecurity community, highlighting the vulnerabilities that organizations face from crypto-funded scams. Microsoft’s findings emphasize the need for enhanced security measures to protect against such targeted attacks.
Related
SecurityEtherscan Introduces Transaction Debugger for Enhanced Ethereum Transaction Analysis
SecurityNvidia Invests $250 Million in UK AI Agent Safety Research Over Five Years
SecurityUK High Court Rules on Bitcoin Seizure from Chinese Fraud Case, Impacting Victims' Claims
SecurityEthereum Researchers Warn of AI Threats to Crypto Security and Offer Protection Strategies
SecurityMicrosoft Introduces Execution Containers to Enhance AI Security
SecurityMEXC Expands Guardian Fund with Additional 1,000 BTC for User Protection
Comments
Comments are moderated before publish.
No comments yet — be the first.